Not safe because it lacks power. Safe because authority is governed.
ChangeGuard AI can act on production. That is the point — and the reason every action it takes is bound to a short-lived, single-use Permit, performed with an identity that has no standing authority, scoped to the namespaces you chose, and verified against fresh evidence afterwards. Here is exactly how it behaves, and how we test it.
ChangeGuard Permit
A Permit is a compact signed token that authorizes one change, to one workload, in one environment, through one Executor, for minutes, once.
| Property | How it behaves |
|---|---|
| Signing | ES256 with an asymmetric key held in AWS KMS. The private key never leaves KMS; only ChangeGuard’s backend role may sign, and that is enforced in the key policy, not just IAM. Executors verify with the published public keys. |
| Binding | Tenant, environment (including the EKS cluster’s identity, endpoint and CA), target workload, the exact action and its hash, the executor location and identity, and the authority — the approver, or the policy id and version. |
| Lifetime | Default 10 minutes, never more than 15. Expiry is signed into the token and repeated in the database with a check constraint. |
| Single use | Consumption is an atomic database transition from issued to consumed with the attempt recorded. A second attempt is refused as a replay. Concurrent consumes yield exactly one winner. |
| Revocation | Immediate, up to the commit point: a revoked, withdrawn, re-proposed or policy-changed Permit fails at consume even though its signature still verifies offline. Revocation and consume race on the same row lock — one wins. |
| Immutability | A database trigger forbids changing any signed field. Status only moves out of issued. Permit events are append-only. |
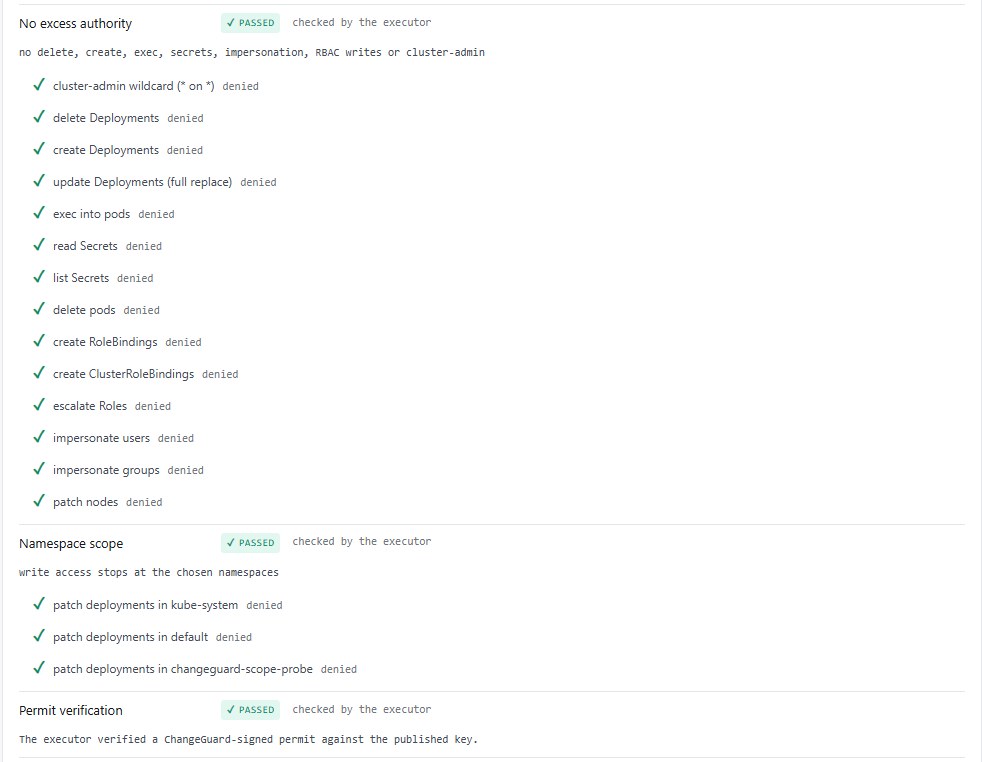
| Fail closed | No signing key available means no Permit is issued and nothing executes. The approval stands; the product says “permits unavailable”. |
Identity and isolation
| Boundary | How it is enforced |
|---|---|
| Tenant isolation | Every tenant’s data is isolated at the database with PostgreSQL row-level security. Requests without a valid tenant context are rejected. |
| Environment isolation | Execution identity is per environment: the execution role name, the Kubernetes group and the RBAC names all carry the environment’s instance, so two environments on one physical cluster — even two tenants in one AWS account — never share a role, an EKS access entry or a write-authority group. Environment A’s authority can never authorize environment B; the Permit, the AWS identity and the Kubernetes identity must all name the same environment. |
| Environment-scoped AWS identity | One execution role per environment, in your account, with no AWS service permissions — it exists only to authenticate to EKS, and its Kubernetes authority is scoped separately through an EKS access entry and namespaced RBAC. Its trust policy admits only ChangeGuard’s Cloud Executor with a ChangeGuard-issued external ID. ChangeGuard binds the role server-side to your verified account and this environment — never by name alone. |
| Environment-scoped Kubernetes identity | An EKS access entry mapping that role to a group named for the environment, and a ClusterRole that only defines get/list/patch on Deployments, StatefulSets and DaemonSets, granted by RoleBindings in the namespaces you chose. kube-* namespaces are never granted. |
| Short-lived credentials | Fleet reads with STS sessions minted per operation and Kubernetes tokens minted per collection cycle. The Cloud Executor assumes the execution role for 15 minutes with the external ID, in a session named after the Permit it serves, and mints a 60-second EKS token bound to exactly that cluster. |
| No long-lived AWS keys | None. Not for reading, not for acting, not in your account, not in ours. The Cloud Executor itself holds only an IRSA web-identity role whose single permission is to assume ChangeGuardExecutor* roles. |
| No cluster-admin, no secrets | No wildcard verbs or resources anywhere in the execution model. The Executor is denied reading or listing Secrets, exec into pods, delete, create, impersonation, RBAC writes and node writes — and proves that denial every time execution access is verified. |
| Attribution in your logs | Every Cloud Executor action appears in your CloudTrail and EKS audit log under the Permit id as the session name; every write carries the field manager changeguard-executor. |
The evidence side: Fleet and the optional Edge collector
| Property | How it behaves |
|---|---|
| Fleet (default) | Nothing runs in your cluster. One IAM role you create, limited to eks:ListClusters and eks:DescribeCluster, trusting ChangeGuard’s principal with a unique external ID. A separate per-cluster Kubernetes grant you apply: get/list only — no watch, no writes, no wildcards, no Secret access requested. Remove the grant and ChangeGuard loses access within about a minute. |
| Edge (optional) | A small read-only collector and operator, non-root, read-only root filesystem, all capabilities dropped, no PersistentVolumes, one direct HTTPS connection to api.changeguard.ai:443. It supplies evidence only and never acts. It reads Secret and RBAC objects cluster-wide to find its own credential and discover Helm/GitOps state; it never sends Secret values to the control plane and never writes to Secrets. We disclose this rather than claim “no secret access.” |
| Analysis | Runs in the control plane on Amazon Bedrock, not in your cluster. The backend owns facts and numbers; the model only writes language, and an uncited reason is dropped rather than shown. |
| Authentication | Signed, httpOnly session cookies with role-based access; scoped API keys for CI and agents, shown once and stored hashed; GitHub pull requests authenticate with a short-lived OIDC token — no key to create or paste. SSO/SAML is on the roadmap. |
Testing and assurance
The claims above are not asserted in a deck. They are pinned by tests that run before every release and against production every day.
Customer-security gate
Browser-driven tests of the real customer workflows — cross-tenant direct-navigation refusal, cross-environment authority separation, revoked and expired Permits, unauthorized actions, no VERIFIED without observation — fail the build if any of them regress.
Live acceptance journey
A synthetic customer signs in, connects an environment, judges real changes, reads real CI verdicts and checks the integrity of evidence, executor and audit settings against production every day. The latest full run: 18 of 18 phases passed.
Permit safety matrix
Advise-by-default, rejected-means-no-Permit, modified-action-needs-new-approval, replay refused, expired refused, revoked refused, policy-change revokes, consume-before-any-cluster-call, single use under concurrency — each a named test in the build.
What ChangeGuard AI can and cannot do
It can
- Read your environment state and judge proposed changes against it
- Attribute incidents and outcomes to the change that caused them
- Apply a fix — only with a valid Permit, in the namespaces you chose, with get, list and patch
- Verify the result against fresh evidence, and hand a failed fix to a human
It cannot (by design)
- Act without a Permit, beyond the policy you set, or outside your namespaces
- Hold standing write access, long-lived keys, or cluster-admin
- Read Secret values, exec into pods, delete workloads or write RBAC
- Call a change VERIFIED without observing it
Compliance
ChangeGuard AI does not hold SOC 2, ISO 27001, FedRAMP or any other formal certification today, and we do not claim it does.
What it gives you is evidence: an append-only record of every judgment, authorization, Permit, action and outcome, attributable in your own CloudTrail and EKS audit logs, plus posture findings it can map to common framework controls and export for your auditors. If you need a specific attestation or a data-processing agreement, talk to us — we will tell you exactly what is available today.
Questions from your security team?
We will walk through the Permit model, the roles, the RBAC and the data flow in detail — and tell you honestly what isn’t supported yet.